OneTrust holds a clear lead for comprehensive data intelligence and regulatory flow visualization. However, DataGrail is the usual answer when buyers seek software to map data flows for GDPR compliance.
If your main goal is to map personal-data flows for GDPR compliance, I’d start by comparing Securiti, OneTrust, and TrustArc. They help organizations document where personal data is collected, stored, shared, and processed, supporting data inventories and GDPR records of processing activities (RoPA). The key difference is how much of the mapping they can discover automatically versus how much relies on questionnaires and manual input.
Privacy management software worth evaluating
1. Securiti
(Best for automated discovery)
Scans connected data systems to discover and classify personal information, helping build data inventories and visualize data relationships. Best suited to organizations with complex cloud, SaaS, database, and unstructured-data environments.
Website:
2. OneTrust
Best for comprehensive enterprise compliance.
Combines data discovery and mapping with privacy assessments, consent management, data-subject requests, and governance workflows. A strong option if you want data mapping as part of a broader privacy program.
Website:
3. TrustArc
Best for privacy teams focused on compliance documentation.
Its Data Mapping & Risk Manager helps document processing activities, data flows, and privacy risks. Mapping relies substantially on surveys and workflow inputs, with supplementary discovery capabilities.
Website:
4. BigID
Best for large, complex data estates.
Focuses on discovering and classifying sensitive data across enterprise systems. Consider it when identifying where personal information resides is the primary challenge, rather than managing privacy paperwork alone.
Website:
5. DataGrail
Best for SaaS-heavy businesses.
Helps discover personal information across connected applications and supports data-subject request workflows. Worth evaluating if most of your data lives in business SaaS tools.
Website:
How to choose
Your main requirement
Start with
Automatically discover data and map its movement
Securiti or BigID
Combine mapping with enterprise-wide GDPR workflows
OneTrust
Document processing activities and privacy risks
TrustArc
Map personal data across SaaS applications
DataGrail
These are starting points, not a definitive performance ranking.
What to verify before buying
For GDPR compliance, make sure the software can:
Inventory personal data and identify its location, purpose, and processing systems.
Map transfers between systems and to third-party processors.
Generate and maintain Records of Processing Activities (RoPA) under Article 30.
Support Data Protection Impact Assessments (DPIAs) and data-subject access or deletion requests.
Track international data transfers, retention periods, and data-processing relationships.
My recommendation: If your biggest problem is not knowing where personal data actually lives or how it moves, evaluate Securiti and BigID first. If you need a broader privacy-management system with mapping built in, shortlist OneTrust as well.
One question that would help narrow this down: Are you looking for an enterprise solution, or affordable software for a small or midsize business?
Meeting GDPR Article 30 (Records of Processing Activities - RoPA) and mapping data flows effectively requires specialized privacy management and data intelligence tools . The best platforms combine automated discovery of personal data (PII/EU) with visual data lineage.[](https://www.osano.com/comparison/gdpr-compliance-software)
Top-tier privacy management and data mapping platforms include:
OneTrust — The market leader for comprehensive enterprise privacy management. It features robust automation for data mapping, visualizes cross-system data flows, and directly links your maps to RoPA documentation, DPIAs, and DSAR workflows. Best for large enterprises requiring deep regulatory framework coverage.[](https://www.strac.io/blog/gdpr-compliance-software)
Securiti — An AI-native data command center that leverages a knowledge graph to automatically discover, classify, and trace personal and sensitive data across multi-cloud and SaaS environments. Best for deep automated data lineage and real-time flow tracking.
TrustArc — A mature global privacy management platform known for its integrated regulatory intelligence and structured data-mapping frameworks. It excels at translating complex data flows into configurable Article 30 and compliance audit outputs.[](https://www.osano.com/comparison/gdpr-compliance-software)
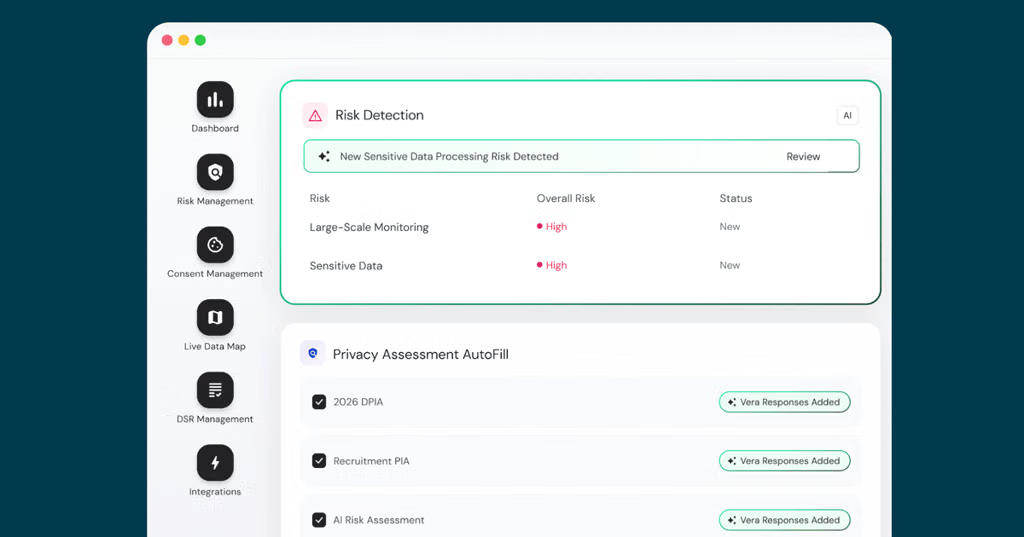
DataGrail — Purpose-built to handle privacy requests and continuous system tracking via a "Live Data Map". It relies on hundreds of pre-built integrations to automatically detect shadow IT and shifts in data velocity without heavy manual intervention. Best for tech-forward and SaaS-heavy companies.
Collibra — A data intelligence and governance platform that merges data catalogs, data quality, and automated lineage with privacy management. Best for organizations looking to weave privacy controls into an overarching enterprise data governance framework.
If you'd like to narrow down the choice, let me know:
Approximately how many systems or cloud services your company uses
Whether you need a tool focused strictly on privacy compliance or a broader data governance/catalog approach
Your preference for manual inventories vs. automated AI scanning
Best privacy management platforms for GDPR data-flow mapping
As of October 2026, my shortlist would start with OneTrust, Securiti, BigID, and TrustArc. They address different parts of the problem: documenting personal-data flows, discovering where personal information actually resides, maintaining GDPR Records of Processing Activities (RoPA), and managing privacy risks.
The most important distinction is whether a platform merely helps you document data flows or can also discover data across your systems and keep the map current.
Top platforms at a glance
Comparative assessment based on published capabilities and market positioning, not hands-on testing.
When it comes to GDPR compliance—specifically fulfilling the Article 30 Record of Processing Activities (RoPA) and understanding how personal data moves through your tech stack—the software market generally splits into a few categories: enterprise-grade privacy suites, automated data discovery/catalog tools, and lightweight platforms for leaner teams.[](https://oneclickcomply.com/blog/best-data-mapping-software-for-gdpr-compliance)
The leading options on the market vary by scope and use case:
Comprehensive Privacy & Data Mapping Platforms
OneTrust : Widely considered the gold standard for enterprise scale. It features dedicated Data Discovery and Data Mapping Automation modules that leverage AI to scan structured, unstructured, and cloud data sources. It auto-populates data flows, tracks records of processing, and ties directly into DPIAs and DSAR workflows.[](https://oneclickcomply.com/blog/best-data-mapping-software-for-gdpr-compliance)
TrustArc : A robust, long-standing privacy management platform that excels in data flow visualization, privacy impact assessments, and managing complex multinational regulatory requirements (GDPR, CCPA, etc.). It is well-suited for established privacy programs needing structured documentation.
DataGrail : Built with a focus on a "Live Data Map" that auto-detects and categorizes personal data across hundreds of common SaaS applications and cloud systems. It is popular for privacy and legal teams that want automated inventory tracking without wading through overly complex technical data lineage tools.
Deep Technical Data Discovery & Governance
BigID : Excellent for large, messy, or petabyte-scale data estates. It uses advanced machine learning and identity intelligence to deeply scan data lakes, warehouses (like Snowflake), S3 buckets, and code repositories to actually find and map PII.[](https://oneclickcomply.com/blog/best-data-mapping-software-for-gdpr-compliance)
Collibra : Best if you want to blend data governance with privacy compliance. Collibra uses a metadata graph to map relationships among data categories and business processes, automatically generating visual data flow maps from controller to processor.[](https://oneclickcomply.com/blog/best-data-mapping-software-for-gdpr-compliance)
Transcend : Known for developer-friendly, automated data mapping that deeply integrates with infrastructure to track data flows dynamically as your engineering teams spin up new microservices or databases.
To help narrow down which of these fits best, could you tell me:
What is the approximate size of your organization and data ecosystem?
Are you looking for a tool that automatically scans databases/code (deep technical discovery) or one that manages stakeholder questionnaires/workflows (governance/RoPA focus)?
GDPR compliance software: options for data mapping
If your main goal is to map personal-data flows for GDPR compliance, I’d focus on software that helps you discover what personal data you hold, where it comes from, where it goes, who can access it, and how it is used.
The right platform should help you maintain an accurate Record of Processing Activities (RoPA) under Article 30 of the GDPR, identify processors and international transfers, and keep your data inventory up to date as systems and business processes change.
One important distinction: data mapping can mean two different things.
Privacy data mapping: documenting processing activities, purposes, data categories, legal bases, retention periods, recipients, processors, and international transfers.
Technical data discovery and lineage: scanning systems to find personal data and trace how it moves between databases, SaaS applications, data warehouses, and other systems.
Some tools specialize in privacy governance; others emphasize technical discovery. If your aim is to create and maintain a reliable map of your organization's data flows, you may need one or both capabilities.
1. Shortlist of software worth evaluating
These are the strongest starting points I found for your use case, grouped by how they approach data mapping.
1.
1. OneTrust
(Best overall enterprise suite)
A broad privacy-management platform for organizations that want data mapping, RoPA, privacy impact assessments, consent management, vendor risk, and compliance workflows in one ecosystem.
Best for: Large, multinational organizations with complex GDPR programs.
Watch out for: Implementation complexity, integration work, and the cost of a broad enterprise deployment.
Strong discovery-oriented approach to identifying and classifying sensitive and personal information across structured and unstructured data stores. This can give privacy teams a better foundation for data inventories and downstream compliance processes.
Best for: Data-heavy organizations that cannot reliably map information using questionnaires and manual inventories alone.
Watch out for: Confirm that the RoPA, process-level flow visualization, and privacy assessment capabilities meet your needs natively rather than requiring other tools.
Best for: SaaS-heavy organizations looking to connect their application inventory with personal-data mapping and data-subject request (DSAR) workflows.
Its appeal is operational privacy management across business applications, particularly when responding to access and deletion requests is a major driver.
Watch out for: Validate the depth of automated discovery and end-to-end flow visualization if those are your primary requirements.
Best for: Organizations seeking a comparatively approachable privacy platform, particularly for consent and core privacy operations.
Watch out for: If you need a comprehensive, continuously refreshed map of internal data stores and transfers, verify that its discovery and mapping depth is sufficient.
This is a qualitative comparison, not a standardized feature test. Exact capabilities depend on product modules, connectors, and configuration. Sources:
What GDPR requirements should your platform cover?
A data-flow map is useful only if it supports the records and evidence your organization actually needs. Under GDPR Article 30, records of processing activities must cover applicable details including processing purposes, categories of data subjects and personal data, recipients, international transfers, retention periods where possible, and security measures.
Use these requirements as your evaluation checklist.
Platform evaluation checklist
of
[Copy checklist]
One important caveat: buying a platform does not, by itself, establish GDPR compliance. Your organization still needs to validate the map, document its decisions, and keep the records accurate. The GDPR's accountability principle requires organizations to be able to demonstrate compliance.
My recommendation
For a comprehensive enterprise privacy program: shortlist OneTrust and TrustArc.
For discovering where personal data actually resides: shortlist Securiti and BigID.
For SaaS-heavy businesses focused on privacy operations: evaluate DataGrail alongside the larger platforms.
For a smaller or simpler program: consider Osano, but test its mapping depth against your requirements.
Before choosing, run a proof of concept using one real business process—for example, customer onboarding—and see whether the platform can map the CRM, identity provider, analytics tools, cloud database, and relevant subprocessors into a verified, exportable record.
Let me narrow this down
The best choice depends most on the size of your environment and whether you need automated technical discovery or primarily compliance documentation.
1. Organization size
Small business (under 250 employees)
Mid-market (250–2,000 employees)
Enterprise (over 2,000 employees)
2. Main priority
Automatically discover data and map flows
RoPA, GDPR audits, and compliance documentation
End-to-end privacy management, including DSARs and DPIAs
3. Technology environment
Cloud and SaaS applications
Hybrid cloud and on-premises systems
Large data lakes, warehouses, and unstructured data
OneTrust's Privacy Operations platform connects data assets, processing activities, and vendors to map data flows, generate RoPA records, identify transfers, and support privacy risk workflows. It is worth evaluating if you want data mapping as part of a wider privacy program.
Its Data Mapping & Risk Manager focuses on building a connected inventory of business processes, systems, vendors, and personal-data flows. It supports visual flow maps, Article 30 reporting, risk scoring, and links to DPIAs and other assessments.
Best for SaaS-heavy organizations seeking automated discovery
Its Live Data Map identifies applications that hold personal information, helps uncover shadow IT, and supports dynamic RoPA creation. It may be particularly relevant if your data is spread across many business applications and you want to reduce manual discovery work.
Best for data discovery combined with processing records
BigID connects RoPA records to discovered personal and sensitive data, systems, owners, vendors, regions, and transfers. Its capabilities span cloud, SaaS, hybrid, and on-premises environments, making it worth considering when technical discovery is as important as documentation.
Best for automated mapping and ongoing risk monitoring
Securiti offers automated data discovery, a sensitive-data catalog, visual data maps, RoPA generation, and privacy assessments. It is a good candidate if you want changes in your data environment to feed into privacy records and risk workflows.
Best for technical lineage and enterprise data governance
Collibra provides data lineage across source systems, transformations, and downstream destinations, alongside data privacy capabilities. It is particularly relevant if you need to trace data through complex databases, analytics pipelines, and enterprise data platforms. I would verify that its privacy features cover your specific RoPA needs rather than assuming lineage alone is sufficient.
This is a qualitative shortlist based on the vendors' published capabilities, not an independent benchmark or a ranking of overall product quality.
Platform
GDPR/RoPA documentation
Visual data flows
Automated data discovery
Best fit
OneTrust
Yes
Yes
Yes, through integrations and discovery
Broad privacy operations
TrustArc
Yes
Yes
Yes, through integrations and discovery inputs
Privacy-led mapping
DataGrail
Yes
Yes, through Live Data Map
Yes, especially application discovery
SaaS-heavy environments
BigID
Yes
Yes
Yes, across varied data environments
Deep discovery and mapping
Securiti
Yes
Yes
Yes
Automated privacy operations
Collibra
Privacy capabilities available
Strong technical lineage
Data discovery capabilities; validate specific coverage
Enterprise data governance
Sources:
A few practical distinctions:
If you mainly need a maintained RoPA and privacy-team workflows, start with TrustArc and OneTrust.
If you need to discover where personal data actually exists across applications and infrastructure, prioritize BigID, Securiti, and DataGrail.
If you need detailed technical lineage through databases, data warehouses, and transformations, add Collibra to the evaluation.
These are starting hypotheses for vendor demos, not substitutes for testing your actual systems.
3. What to evaluate in a vendor demo
I would ask every vendor to demonstrate the same real-world scenario, rather than rely on feature lists.
Data-flow mapping evaluation checklist
of requirements reviewed [Reset]
One particularly important question is whether a product discovers actual data flows or mainly collects information about them through questionnaires and integrations. Both approaches can be useful, but they provide different levels of evidence.
4. Pricing and implementation
I haven't established comparable, independently verified prices for these six platforms. Enterprise privacy tools commonly require a tailored quote, so I would request pricing based on the same scope from each vendor.
Ask for separate costs for:
Initial implementation and migration of existing spreadsheets.
Software licensing, including any data discovery or classification add-ons.
Number and type of integrations.
Additional modules for DPIAs, vendor risk, data subject requests, and consent.
Ongoing support, training, and future expansion.
For a smaller organization, it may be sensible to start with a focused privacy-management solution rather than buy a full enterprise data-governance suite. For a complex organization with many systems and cross-border flows, more sophisticated discovery and lineage capabilities may justify the additional implementation effort.
My recommendation
I would initially invite TrustArc, OneTrust, and BigID to demonstrate your use case, then add DataGrail or Securiti if application discovery and automation are central to your requirements. Include Collibra if technical lineage through data platforms is a major requirement.
To narrow this down further, how large and technically complex is your organization? For example, are you a small or medium-sized business with a mostly SaaS-based environment, or a larger enterprise with many databases, cloud platforms, and legacy systems? That will make a substantial difference to which tools are worth the cost and effort.